Professional skills
Elastic Security for SIEM in Zurich
Showing starts assigned to Zurich. Change country or city · Global course
Four-day, 32-hour course to ingest data, query events, build dashboards, triage alerts, and hunt threats in a modern SIEM.
THE BIG PICTURE
About this course
Elastic awards its own product certifications in analysis, observability, and security. This course provides study support for candidates pursuing a security-focused analyst certification pathway from Elastic. Across four days you will ingest data with Agent and Fleet, apply ECS, query in Discover with KQL/EQL, and build Lens visualisations and dashboards. You will then work in the Security App to create and tune detections, triage alerts, use Timeline and Cases, and complete a guided threat hunting capstone with realistic log and endpoint data. Certification exams are purchased and scheduled directly with Elastic via its certification pages. Exact exam format, duration, scoring, delivery method, and validity are set by Elastic and may change; always consult the current official exam guide before booking. Elastic owns the certification scheme. MindClick provides training and exam preparation and is not an accredited or authorised partner.
What you’ll learn
- Onboard endpoint and log data using Agent and Fleet, and verify data streams
- Apply ECS to normalise fields and make data searchable across sources
- Use Discover with KQL to filter, aggregate, and pivot through events
- Build clear Lens visualisations and assemble interactive dashboards
- Configure and tune detection rules, triage alerts, and investigate with Timeline
- Create and manage Cases, linking timelines, notes, and evidence for handover
- Conduct hypothesis-led threat hunts using KQL/EQL across multiple indices
- Identify relevant exam domains and practise exam-style questions to prepare effectively
A CLEAR PATH FORWARD
4-day Elastic Security for SIEM agenda
4 instructor-led days (32 contact hours) mapped to the exam domains. Each day combines short concept sessions, hands-on practice on a running case study and exam-style questions.
- Learning route
- 4 recommended days
- Practical work
- 4 guided activities
- Finish with
- Mock exam + certification exam
Take a look at each day. Open a section to see the topics and practical work.
Day 1Stack and SIEM fundamentalsIngestion, ECS, Discover and data views
What we’ll cover
- 09:00–10:30 · Stack and SIEM architecture, components, and data flow
- 10:45–12:15 · Fleet and Agent deployment; integration policies and data streams
- 13:15–14:45 · Elastic Common Schema (ECS): field sets, mappings, and normalisation
- 15:00–16:00 · Data views and index selection; Discover orientation and saved searches
- 16:00–17:00 · Exam-style practice questions on ingestion, ECS, and Discover
- 17:00–17:30 · Day 1 summary, Q&A, and parking lot items
Put it into practice
Deploy an Agent via Fleet to a lab host, enable common integrations, and validate incoming data streams. Map key fields to ECS and verify queryability in Discover.
You’ll take away
Working lab ingest pipeline and ECS field map
Day 2Querying, visualisations, and dashboardsKQL, Discover, Lens, Dashboards
What we’ll cover
- 09:00–10:30 · Recap and warm-up: KQL filters, queries, and aggregations in Discover
- 10:45–12:15 · Building visualisations with Lens: tables, charts, and gauges
- 13:15–14:45 · Dashboards: layout, drilldowns, annotations, and sharing
- 15:00–16:00 · Saved searches and dashboard-driven investigations
- 16:00–17:00 · Exam-style practice questions on KQL, Lens, and Dashboards
- 17:00–17:30 · Day 2 wrap-up, key takeaways, and open questions
Put it into practice
Design a dashboard for security monitoring using Lens visualisations fed by saved searches. Add filters and drilldowns to support rapid investigation.
You’ll take away
Reusable monitoring dashboard with documented KQL examples
Day 3Detections, triage, Timeline, and CasesSecurity App, rules, alerts, investigations
What we’ll cover
- 09:00–10:30 · Recap; Security App tour: Overview, Alerts, Rules, and Cases
- 10:45–12:15 · Detection rules: rule types, schedules, exceptions, and tuning
- 13:15–14:45 · Alert triage workflow and building investigation Timelines
- 15:00–16:00 · Cases: creating, linking evidence, assignments, and notifications
- 16:00–17:00 · Exam-style practice questions on detections, triage, Timeline, and Cases
- 17:00–17:30 · Day 3 debrief and preparation for hunting capstone
Put it into practice
Create and tune a custom detection rule, generate sample alerts, and triage them into a Timeline. Open a Case, attach evidence and notes, and prepare a brief handover.
You’ll take away
Configured detection rule, sample Timeline, and a documented Case
Day 4Threat hunting capstone and exam readinessThreat hunting, EQL/KQL, response, exam prep
What we’ll cover
- 09:00–10:30 · Recap; threat hunting methodology and hypothesis building
- 10:45–12:15 · Hunting with KQL/EQL: sequences, rarity, and process/network pivots
- 13:15–14:45 · Endpoint and network telemetry investigations; enrichments and context
- 15:00–16:00 · Hunt capstone: execute, document findings, and propose response
- 16:00–17:00 · Mock exam: timed, exam-style questions with group review
- 17:00–17:30 · Exam booking guidance, readiness checklist, and next steps
Put it into practice
Run a guided hunt across multiple indices using KQL/EQL to validate a threat hypothesis and assemble a case narrative. Conclude with a timed mock exam and feedback discussion.
You’ll take away
Hunt report, investigation artefacts, and personal exam study plan
Bring it all together
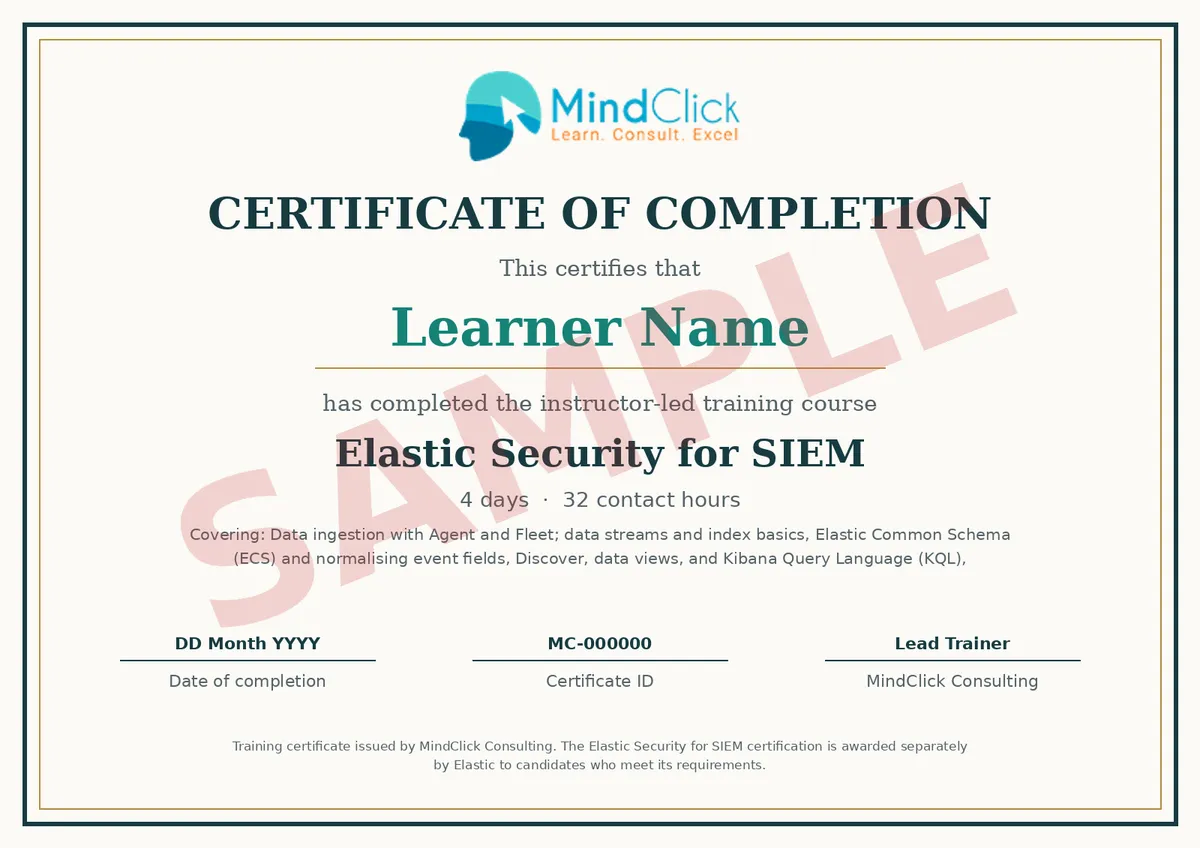
Certification exam: Elastic Security for SIEM, awarded by Elastic. Confirm the current exam format with the awarding body when you book. Every attendee also receives a MindClick certificate of completion for 32 contact hours.
What you receive
You earn two separate credentials. The sample shows the MindClick training certificate.
- MindClick certificate of completion: 4 days, 32 contact hours, issued to every attendee who completes the course.
- Elastic Security for SIEM: issued by Elastic when you meet its requirements and pass the exam.
Before you choose your learning route
Session timings are indicative; the trainer may adjust them for the group. Exam details reflect the awarding body’s published information at the time of writing; confirm the current version when you book.
Elastic owns this certification scheme. MindClick provides training and exam preparation and is not an accredited or authorised partner of Elastic.
Fees
| Delivery format | Fee per learner | Exam fee |
|---|---|---|
| Live online | $2,800 USD ≈ €2,485 |
Included |
| Classroom | $4,500 USD ≈ €3,995 |
Included |
Local amounts are indicative only, converted at the rate captured on 2026-10-02. You are charged in USD and your bank sets the final rate.
One awarding-body certification exam attempt is included in the training fee. Confirm the current fee, any applicable tax and what the fee covers in writing before you pay.
Prerequisites
- No formal certification prerequisites are published. Recommended: familiarity with Kibana, basic KQL, and common Windows/Linux log sources; bring a laptop with a modern browser and local admin rights.
Who is this course for?
- Security analysts monitoring network and host logs through a SIEM.
- SOC engineers working with detection rules and alert triage.
- Threat hunters investigating events with Timeline and Cases.
- Analysts preparing for the Elastic Certified SIEM Analyst exam.
FIND YOUR START
Confirmed batch starts
Choose a published start, then review your offer in the same enrollment flow. A start date is not the full timetable or a seat reservation.
Choose your country & monthStarts
- Training location
- Zurich, Switzerland
- Local timezone
- Europe/Zurich
Venue and full session timetable to be supplied.
Starts
- Training location
- Zurich, Switzerland
- Local timezone
- Europe/Zurich
Joining details and full session timetable to be supplied.
Starts
- Training location
- Zurich, Switzerland
- Local timezone
- Europe/Zurich
Joining details and full session timetable to be supplied.
Starts
- Training location
- Zurich, Switzerland
- Local timezone
- Europe/Zurich
Venue and full session timetable to be supplied.
Starts
- Training location
- Zurich, Switzerland
- Local timezone
- Europe/Zurich
Venue and full session timetable to be supplied.
Starts
- Training location
- Zurich, Switzerland
- Local timezone
- Europe/Zurich
Joining details and full session timetable to be supplied.
Frequently asked questions
How long is the course?
4 days, 32 contact hours, normally 09:00 to 17:30 with breaks. The agenda follows the exam domains and the final day includes a mock exam.
Is the exam included?
Yes. Outside India the fee includes one certification exam attempt. Retakes are booked and paid directly with the awarding body.
What does this course cost?
Outside India this 4-day course is listed at USD 2,800 per learner for live online delivery and USD 4,500 for classroom delivery. Both fees include one certification exam attempt. Pricing for India is confirmed separately by an advisor. Taxes and the final offer are confirmed in writing before you pay.
Are there prerequisites?
No formal certification prerequisites are published. Recommended: familiarity with Kibana, basic KQL, and common Windows/Linux log sources; bring a laptop with a modern browser and local admin rights.
What certificate will I receive?
Two credentials. MindClick issues a certificate of completion for 32 contact hours to every attendee. Elastic issues the Elastic Security for SIEM certification when you pass the exam and meet its requirements.
Is MindClick an accredited training partner for this certification?
MindClick provides training and exam preparation and is not an accredited/authorised partner of Elastic. Elastic administers and sells the certification exams directly via its website.
Where is classroom training delivered?
Singapore and Dubai are the priority classroom markets for this catalog. Classroom delivery is also available in the other listed countries, and live online delivery is available everywhere. Venues are confirmed per booking; a listed city is a training market, not an owned campus.
KEEP EXPLORING
More ways to move forward.
Related training from the course catalog.
Elasticsearch Engineer Training
This 4-day course builds practical skills in designing, indexing, querying, scaling, and operating a distributed search and analytics system.
Data Analysis with Kibana
A 4-day course on analysing data with a visual analytics interface: query, design charts and dashboards, explore time series, maps, ML and alerts.
Elastic Observability Engineer Training
A 4-day course where you ingest logs, metrics and traces, analyse them in dashboards, set alerts, and practise end-to-end incident workflows.
Elastic Security for Endpoint
Investigate host-based alerts from Elastic Defend, enrich security data, and hunt threats on the endpoint.