Certification preparation
CISA Exam Preparation in Muharraq
Showing starts assigned to Muharraq. Change country or city · Global course
A 3-day course to review CISA domains, practise audit scenarios, and work through exam-style questions with feedback and a timed mock.
THE BIG PICTURE
About this course
Certified Information Systems Auditor (CISA) is a global certification for information systems audit, assurance and control professionals, awarded by ISACA. Across three days you review all CISA domains through concise teaching, worked examples and realistic scenarios. You will map audit objectives to risk, walkthrough governance and lifecycle controls, evaluate operations and resilience, and consolidate protection of information assets. Each day includes guided exercises, collaborative debriefs and exam-style question practice, culminating in a timed mock and study planning. The CISA exam consists of 150 multiple-choice questions to be completed in 240 minutes. It is closed book, delivered online via remote proctoring or at test centres, and scored on a 200–800 scale with 450 as the passing score. Registration and scheduling are managed through ISACA. ISACA owns the certification scheme. MindClick provides training and exam preparation and is not an accredited or authorised partner.
What you’ll learn
- Plan a risk-based IS audit engagement aligned to standards and organisational objectives
- Assess IT governance structures, strategy alignment, performance and resource management
- Evaluate controls in system acquisition, development and implementation, including change and configuration management
- Review IT operations, service management and business resilience, including capacity, availability and continuity
- Assess protection of information assets across access control, data protection, monitoring and third-party risk
- Interpret audit evidence using sampling and data analytics, and communicate findings effectively
- Prepare effectively for the CISA exam with timing strategies, question techniques, a study plan and booking steps
A CLEAR PATH FORWARD
3-day CISA Exam Preparation agenda
3 instructor-led days (24 contact hours) mapped to the exam domains. Each day combines short concept sessions, hands-on practice on a running case study and exam-style questions.
- Learning route
- 3 recommended days
- Practical work
- 3 guided activities
- Finish with
- Mock exam + certification exam
Take a look at each day. Open a section to see the topics and practical work.
Day 1Audit planning and IT governanceDomains 1–2
What we’ll cover
- 09:00–09:30 · Course orientation, exam structure, and personal goals
- 09:30–10:45 · Domain 1: IS audit standards, ethics, risk-based planning, and scoping
- 10:45–12:30 · Evidence gathering, sampling methods, data analytics, and documentation
- 12:30–13:30 · Lunch
- 13:30–15:30 · Domain 2: Governance frameworks, strategy alignment, and IT resource management (with short break)
- 15:30–16:15 · Performance, maturity, and reporting; governance of enterprise risk
- 16:15–17:00 · Exam-style practice questions (Domains 1–2) and debrief
- 17:00–17:30 · Daily review, parking-lot items, and next-day preview
Put it into practice
Create a risk-based audit plan for a sample organisation, defining objectives, scope, resources and procedures. Peer review the plan and revise it based on stakeholder scenarios.
You’ll take away
Risk-based audit plan template with worked example
Day 2Acquisition, development, and operationsDomains 3–4
What we’ll cover
- 09:00–09:20 · Recap of Day 1 and clarifications
- 09:20–10:45 · Domain 3: Business case, requirements, feasibility and solution selection
- 10:45–12:30 · Development lifecycles, change and configuration management controls, and testing
- 12:30–13:30 · Lunch
- 13:30–15:30 · Domain 4: Operations and service management, capacity/availability and resilience (with short break)
- 15:30–16:15 · Incident and problem management; disaster recovery and continuity testing
- 16:15–17:00 · Exam-style practice questions (Domains 3–4) and debrief
- 17:00–17:30 · Daily review and preparation for Domain 5
Put it into practice
Walk through a change request from requirements to release and into operations, identifying control gaps and audit tests. Summarise findings mapped to CISA domains.
You’ll take away
Change and operations control review checklist
Day 3Protection of information assets and exam readinessDomain 5 and integrated review
What we’ll cover
- 09:00–09:20 · Recap of Day 2 and key takeaways
- 09:20–10:45 · Domain 5: Security governance, policy, and risk management
- 10:45–12:30 · Controls for identity and access, networks/endpoints, data protection, monitoring, and third-party risk
- 12:30–13:30 · Lunch
- 13:30–15:30 · Timed mock exam under exam conditions (mixed domains)
- 15:30–16:00 · Mock exam quick marking and score interpretation
- 16:00–17:00 · Targeted review of weak areas; high-yield topics, timing and question techniques
- 17:00–17:30 · Exam booking guidance, post-course study plan, and Q&A
Put it into practice
Analyse a simplified environment to map security controls to risks and propose priority remediation. Sit a timed mini-mock and use results to refine a personal study plan.
You’ll take away
Personal exam study plan and control coverage map
Bring it all together
Certification exam: Certified Information Systems Auditor (CISA), awarded by ISACA. 150 multiple-choice questions, 240 minutes, Closed book, Online remote proctored or test centre (PSI). Pass mark: Scaled score of 450 or higher (200–800 scale). Validity: Certification maintenance requires 120 CPE hours over a 3-year cycle (minimum 20 per year) and annual maintenance fees.. Every attendee also receives a MindClick certificate of completion for 24 contact hours.
What you receive
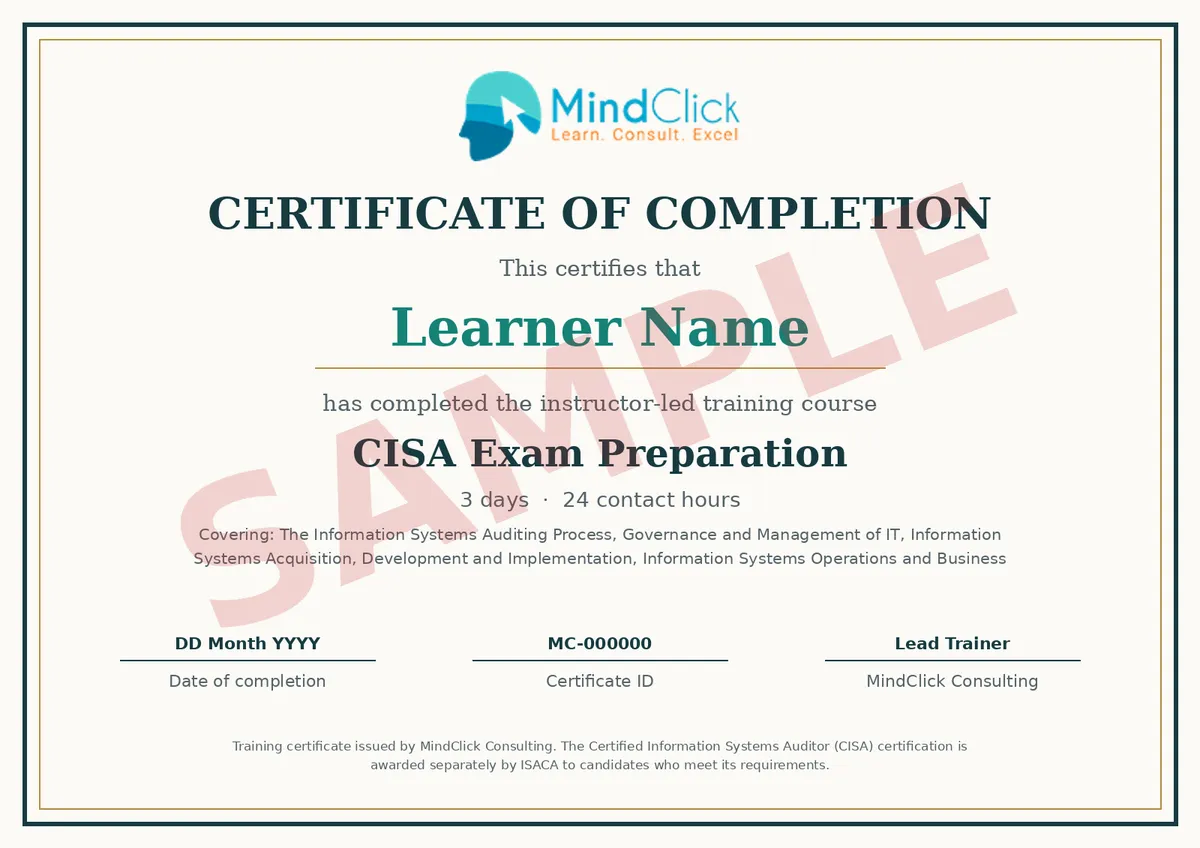
You earn two separate credentials. The sample shows the MindClick training certificate.
- MindClick certificate of completion: 3 days, 24 contact hours, issued to every attendee who completes the course.
- Certified Information Systems Auditor (CISA): issued by ISACA when you meet its requirements and pass the exam.
Before you choose your learning route
Certification route: Earning CISA also requires verified professional experience and an application to ISACA; passing the exam alone does not grant the credential.
Session timings are indicative; the trainer may adjust them for the group. Exam details reflect the awarding body’s published information at the time of writing; confirm the current version when you book.
ISACA owns this certification scheme. MindClick provides training and exam preparation and is not an accredited or authorised partner of ISACA.
Fees
| Delivery format | Fee per learner | Exam fee |
|---|---|---|
| Live online | $2,800 USD ≈ AED 10,280 |
Included |
| Classroom | $4,500 USD ≈ AED 16,530 |
Included |
Local amounts are indicative only, converted at the rate captured on 2026-10-02. You are charged in USD and your bank sets the final rate.
One awarding-body certification exam attempt is included in the training fee. Confirm the current fee, any applicable tax and what the fee covers in writing before you pay.
Prerequisites
- No formal prerequisites to sit the CISA exam. To earn the certification, ISACA requires at least five years of relevant IS audit, control or security experience (with certain substitutions allowed). Bring a laptop with a modern browser; relevant workplace policies or risk registers are optional for discussion.
Who is this course for?
- Professionals and teams evaluating this subject for their work.
FIND YOUR START
Confirmed batch starts
Choose a published start, then review your offer in the same enrollment flow. A start date is not the full timetable or a seat reservation.
Choose your country & monthStarts
- Training location
- Muharraq, Bahrain
- Local timezone
- Asia/Bahrain
Joining details and full session timetable to be supplied.
Starts
- Training location
- Muharraq, Bahrain
- Local timezone
- Asia/Bahrain
Joining details and full session timetable to be supplied.
Frequently asked questions
How long is the course?
3 days, 24 contact hours, normally 09:00 to 17:30 with breaks. The agenda follows the exam domains and the final day includes a mock exam.
What is the exam format?
Certified Information Systems Auditor (CISA): 150 multiple-choice questions, 240 minutes, Closed book, Online remote proctored or test centre (PSI). Pass mark: Scaled score of 450 or higher (200–800 scale). Confirm the current version with the awarding body when you book.
Is the exam included?
Yes. Outside India the fee includes one certification exam attempt. Retakes are booked and paid directly with the awarding body. Earning CISA also requires verified professional experience and an application to ISACA; passing the exam alone does not grant the credential.
Are there prerequisites?
No formal prerequisites to sit the CISA exam. To earn the certification, ISACA requires at least five years of relevant IS audit, control or security experience (with certain substitutions allowed). Bring a laptop with a modern browser; relevant workplace policies or risk registers are optional for discussion.
What certificate will I receive?
Two credentials. MindClick issues a certificate of completion for 24 contact hours to every attendee. ISACA issues the Certified Information Systems Auditor (CISA) certification when you pass the exam and meet its requirements. Certification maintenance requires 120 CPE hours over a 3-year cycle (minimum 20 per year) and annual maintenance fees..
Is MindClick an accredited training partner for this certification?
MindClick provides training and exam preparation and is not an accredited/authorised partner of ISACA; ISACA administers the CISA exam and scheduling.
KEEP EXPLORING
More ways to move forward.
Related training from the course catalog.
Certified Information Systems Security Professional (CISSP)
Five-day course covering the eight CISSP domains with labs, case studies and daily exam practice to build confidence for certification.
Certified Ethical Hacker (CEH)
Five-day course to practise ethical hacking: reconnaissance, scanning, exploitation, web and wireless attacks, with hands-on labs and exam prep.
CompTIA Security+
A 4-day course building Security+ skills through labs on threats, architecture, operations and governance, with daily exam practice.
Certified Information Security Manager (CISM)
Five-day course where learners practise information security governance, risk, programme delivery and incident response, with labs and exam prep.